Rails Patches a CVSS 9.8 Active Storage Flaw Letting Uploads Write and Read Server Files
The Rails core team shipped versions 8.1.4.1 and 8.0.5.2 on 4 November 2026, fixing a critical ImageMagick coder flaw in Active Storage alongside 20 other security issues.
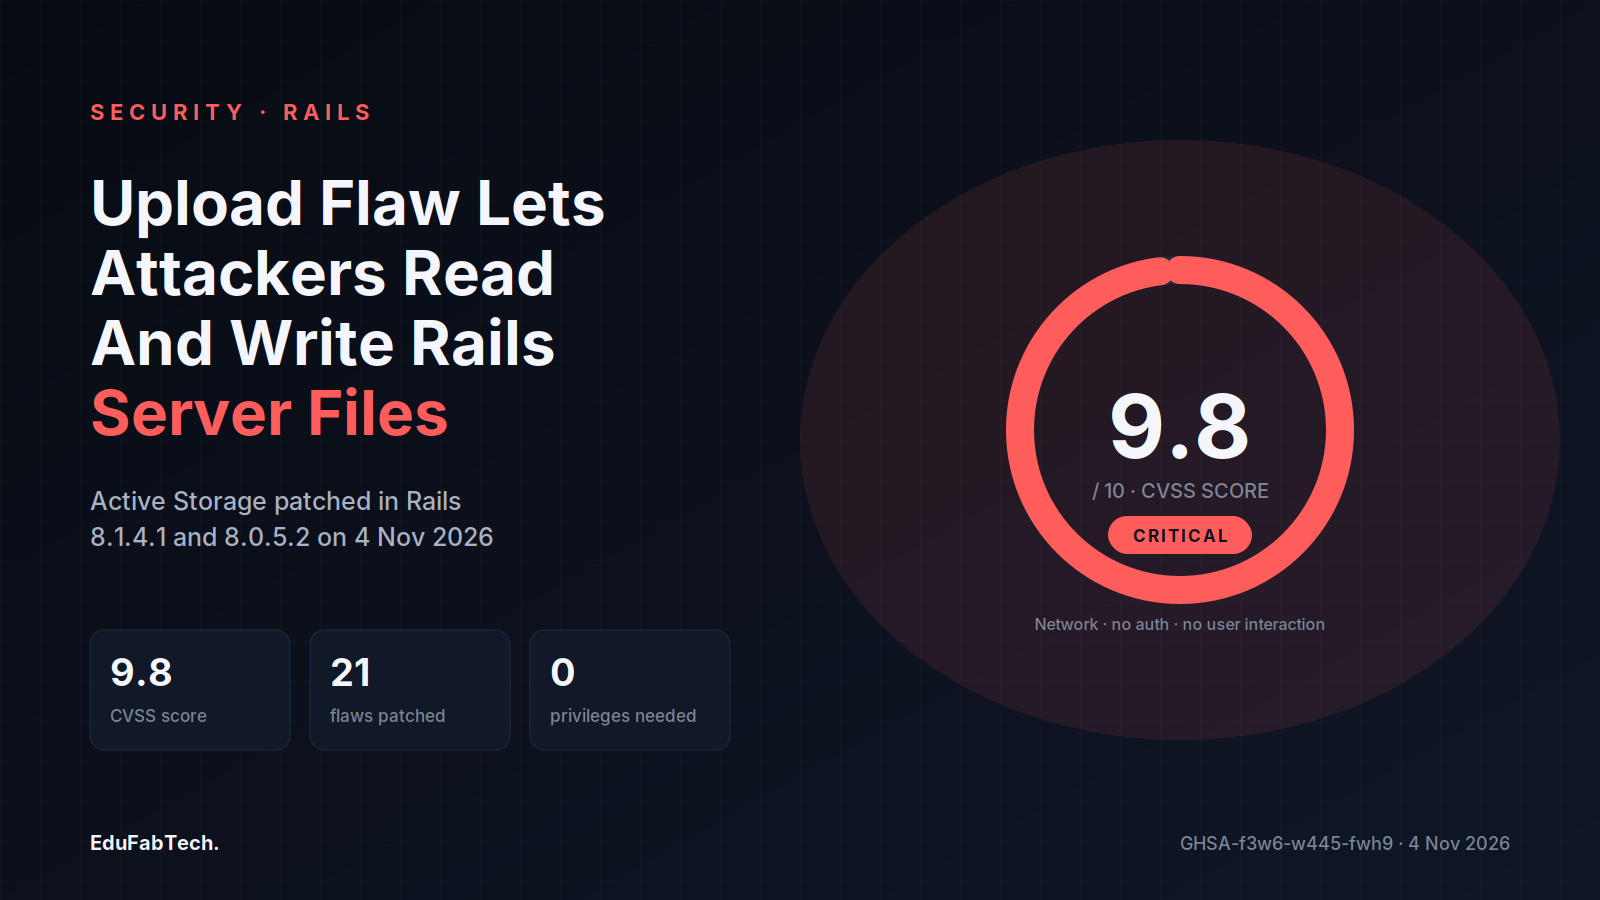
Ruby on Rails' core team released versions 8.1.4.1 and 8.0.5.2 on 4 November 2026, a coordinated security update that closes 21 vulnerabilities, the most serious of which let an unauthenticated attacker write, and in many configurations read, arbitrary files on a Rails server through its Active Storage file-upload system, according to the release notes published on the Ruby on Rails blog.
The flaw, tracked as GHSA-f3w6-w445-fwh9, carries a CVSS score of 9.8 out of 10, according to the advisory the Rails security team published on GitHub Security Advisories in November 2026. Its vector marks the attack as reachable over the network, requiring low attacker skill, no privileges and no user interaction, with the maximum possible impact on confidentiality, integrity and availability. It affects Active Storage before version 8.0.5.2, and the 8.1 line before 8.1.4.1.
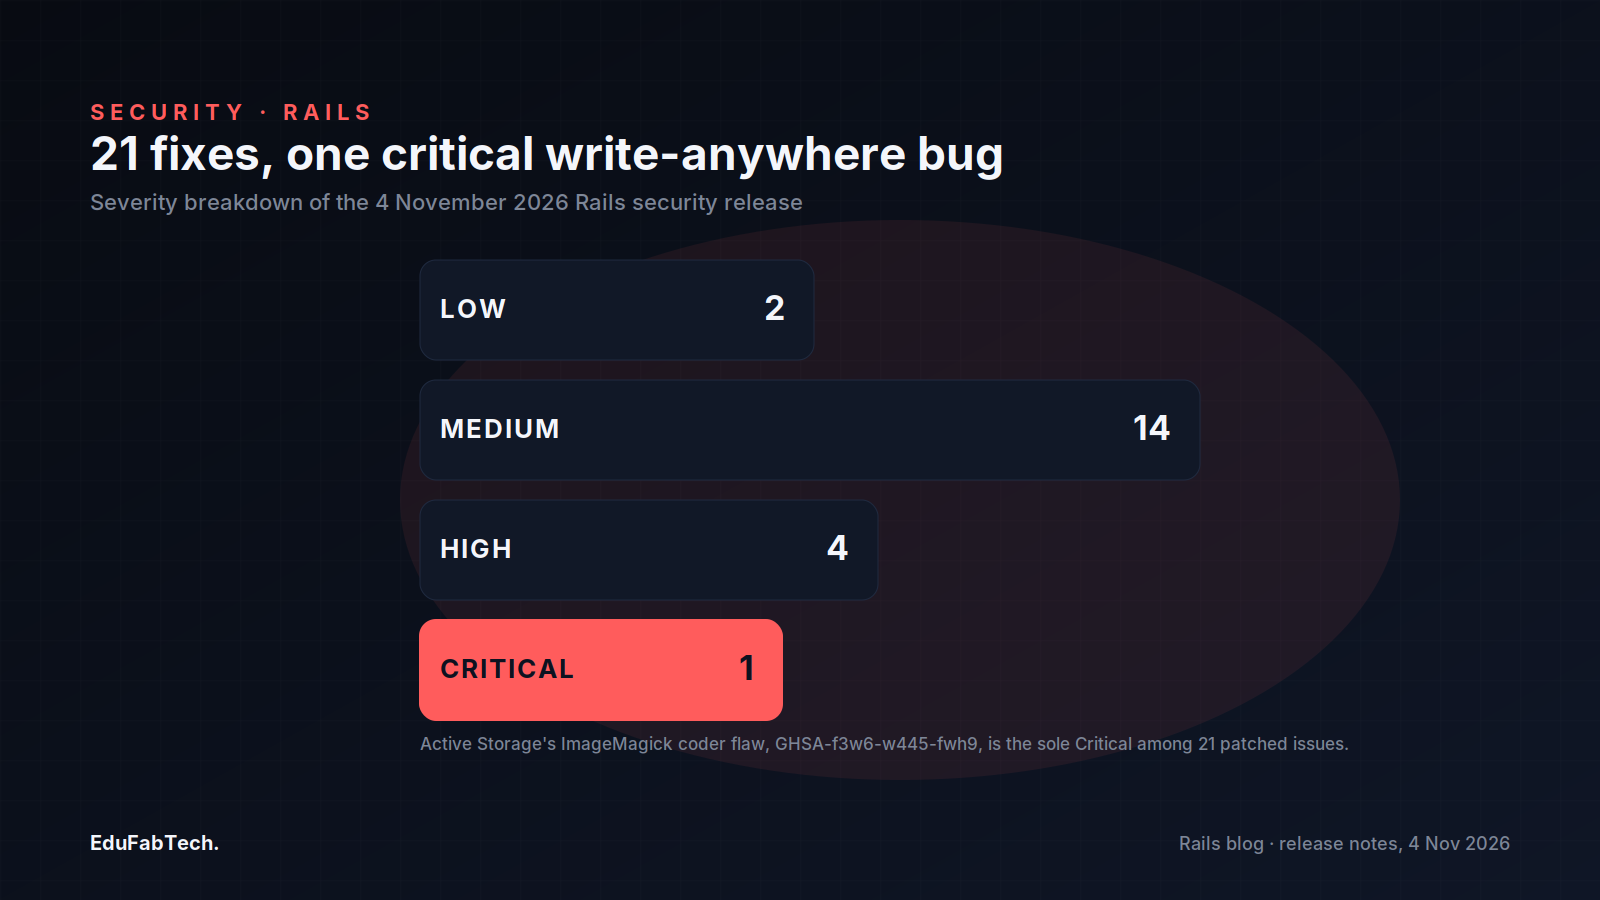
Rails bundled the fix with 20 other issues in the same release, by the Rails blog's November 2026 count: four rated high, fourteen medium and two low, spanning Active Storage's video and image previews, a Strong Parameters bypass, IP spoofing through the Forwarded header in the 8.1 line, and cross-site scripting in several Action View helpers.
How a file upload could reach a file-writing script
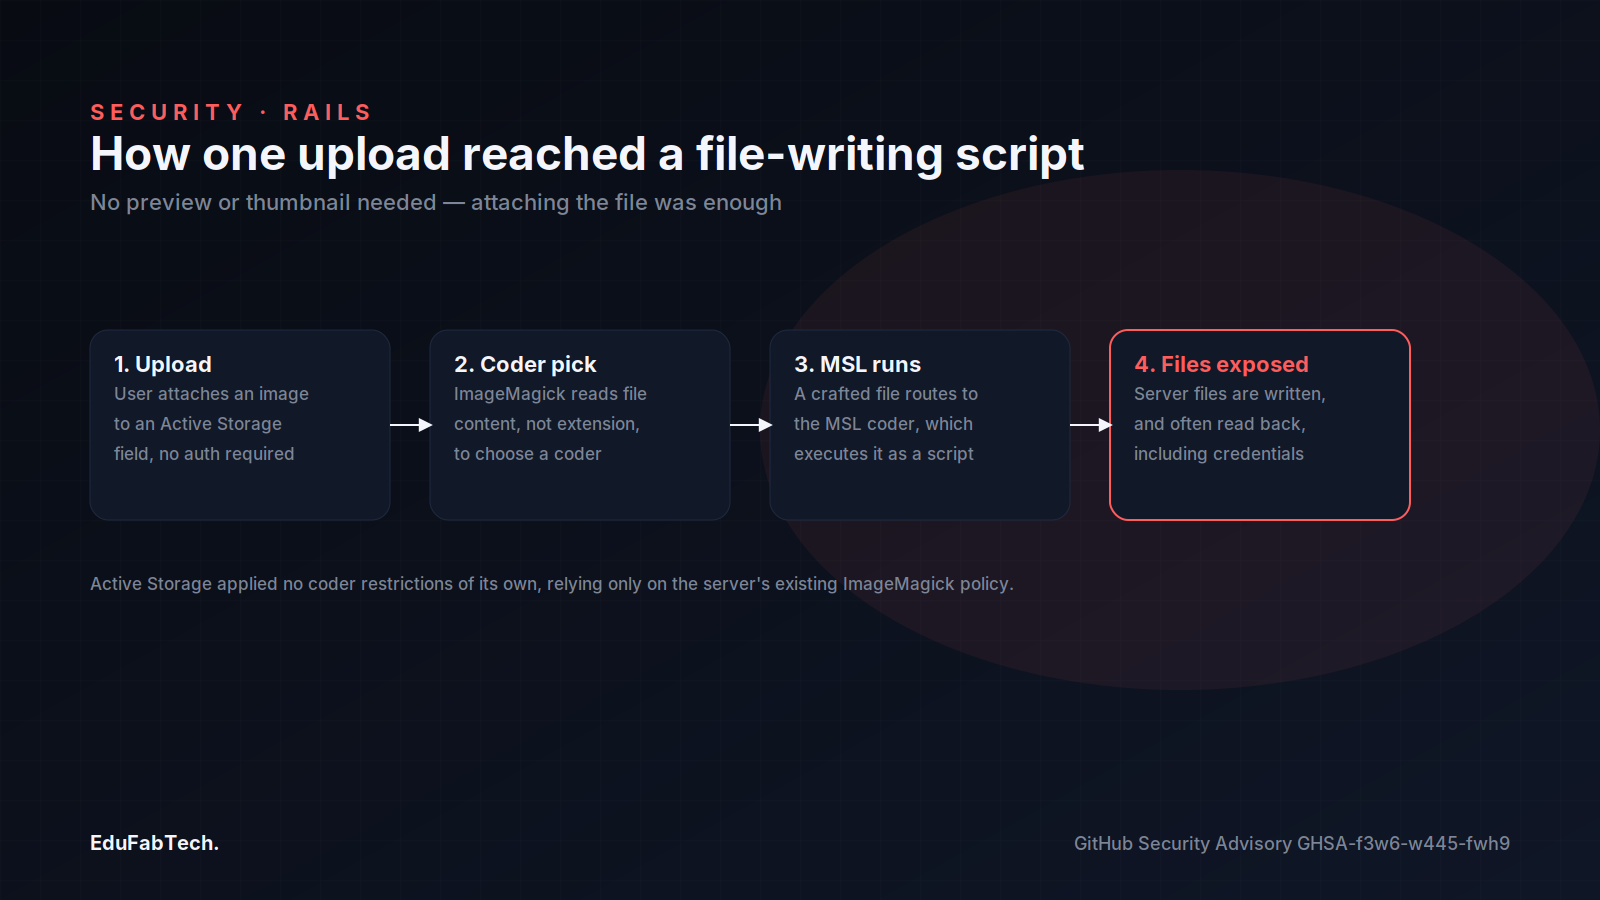
Active Storage, Rails' built-in library for attaching uploaded files to database records, calls ImageMagick to analyse an image as soon as it is attached, before any thumbnail or preview is generated, the GitHub advisory states. ImageMagick picks which internal format handler, or "coder," to use based on the content of a file rather than its extension or declared type, so a file that looks like an ordinary image can still be routed to a coder meant for something else.
One of those handlers, ImageMagick's MSL coder, treats its input as a script that can name files to read or write, the advisory says. Because Active Storage did not restrict which coders an upload could reach, relying only on whatever policy the server's ImageMagick installation already had, a crafted upload reaching the MSL coder could write a file to the server and, when the application stored attachments with Active Storage's Disk service, read files the application process could read, including its secret_key_base, database passwords and other credentials, according to the advisory.
The Hacker News report on the disclosure notes that reaching the vulnerable code path required nothing beyond attaching the file, with no variant or preview needed, and that the flaw depends on an application using ImageMagick, through the mini_magick gem, as its variant processor, which has been Active Storage's default for applications loading defaults from Rails 6.1 or earlier.
Who reported it, and what the patch changes
The GitHub advisory credits the discovery to security researcher RyotaK, who disclosed the issue through HackerOne; the Rails security team verified the report before issuing the fix.
The patched versions ship an ImageMagick security policy that Active Storage now applies to every MiniMagick process, denying the MSL coder along with other coders that touch files, Ghostscript-backed coders, and the @filename indirection feature that can redirect ImageMagick to read a different file than the one it was given, the advisory states. Applications must also upgrade the mini_magick gem to a version that applies the new policy. The Rails blog post recommends every affected application upgrade as soon as possible, and notes that security support for the 8.0 series ends on 7 November 2026, three days after the patch shipped.
Why it matters beyond the Rails community
Active Storage ships inside Rails itself rather than as an optional add-on, so any Rails application that accepts image or video uploads with default settings and Disk storage was within reach of the flaw. Rails remains a common framework in introductory web-development courses and a frequent choice for research groups building internal data-collection tools, lab portals and departmental web applications, contexts where a bug in a default-on component is easy to overlook compared with a bespoke upload handler a team wrote and reviewed itself.
For developers maintaining or teaching with Rails, the practical step from the disclosures is to confirm an application has moved to 8.1.4.1 or 8.0.5.2, update the mini_magick gem to a compatible release, and check, as the Hacker News report on the advisory suggests, that the deployed ImageMagick policy actually blocks the coders the patch is meant to deny rather than assuming the gem upgrade alone is sufficient.
A quick question for readers
Which skill will matter most for getting a job in 2030?
Everyone has a prediction. Add yours and see what students are betting on.
Pick an answer, create a free account in a minute, and your vote counts. Already a member? Sign in
Comments 3
Comment-
The part that stands out is how Active Storage reached ImageMagick's MSL coder before any thumbnail or preview even existed - just attaching…
-
The part that actually explains why this is so bad is the attack chain: ImageMagick picking a coder by content-sniffing rather than extensio…
-
The detail that'd stop me mid-coffee is that the vulnerable path triggers on attach alone, no thumbnail or preview needed. That's the kind o…
Join free to read the full comments and reply Comments are between members; an account takes a minute.
Source: Ruby on Rails
Sources (3)
- Ruby on Rails core team. Rails Versions 8.0.5.2 and 8.1.4.1 have been released!. Ruby on Rails (official blog), 2026. rubyonrails.org ↗ · checked 5 Nov 2026
- Rails security team. GHSA-f3w6-w445-fwh9: Possible file read and write in Active Storage. GitHub Security Advisories, 2026. github.com ↗ · checked 5 Nov 2026
- The Hacker News. Critical Rails Flaw Lets Attackers Write Server Files via Crafted ImageMagick Uploads. The Hacker News, 2026. thehackernews.com ↗ · checked 5 Nov 2026